


Microsoft 365: Every Way to Find and Review Shared Files
Sharing files through Teams, OneDrive or SharePoint is incredibly easy. Figuring out what users in your organization are sharing and with whom? Not so much. Many organizations struggle to control cloud sharing in M365 – a problem that can be difficult to address with built-in governance tools. This is every option Microsoft 365 provides to help you find and audit shared files.
Shared Access Reports in Microsoft 365
Data Access Governance Reports
Data access governance reports for SharePoint and OneDrive are available as part of the SharePoint Advanced Management feature. Basically, data access governance reports allow you to generate downloadable CSV reports with broad-strokes information on all SharePoint and OneDrive sites in your organization, such as the total number of sharing links or permissioned users on a site.
Note: In order to use SharePoint Advanced Management features, your organization needs to meet one of three prerequisites.
At least one user in your organization has a Microsoft Copilot license.
Your subscription includes the SharePoint Advanced Management add-on.
Your organization has a Microsoft 365 E7 subscription.
Data access governance reports take 24 hours to complete and, depending on the report type, can be run daily or monthly. There are a number of different reports available, split between snapshot reports, which show the current state of sites, and activity reports, which show changes over the last 28 days.
Snapshot reports:
Site permissions report: Lists the total number of permissioned users for each site, as well as the number of sharing links, guest user permissions, Everyone and Everyone Except External Users (EEEU) permissions, Entra ID groups with permissions and items with unique permissions (broken inheritance).
Site permissions for users report: Allows you to choose specific users and generates a list for each user showing all SharePoint sites they can access. The report includes details such as the site URL and admin, as well as a count of files and folders that have been shared with them directly or indirectly through a group.
Sensitivity label for files report: Allows you to choose a sensitivity label and lists SharePoint sites by the number of files the chosen label is currently applied to.
Sites and files shared via special SharePoint groups: Shows every item that can be accessed by the Everyone and Everyone except external users (EEEU) groups built into SharePoint. The only report in this list to give you item-level permissions and details rather than a count.
Activity reports:
Sharing links report: Lists sites where the highest number of new sharing links has been created in the last 28 days. This report is available for Anyone links, People in your organization links and external Specific people links.
Shared with “Everyone except external users” reports: Lists sites where the highest number of items have been shared with the EEEU group in the last 28 days.
Advantages & Disadvantages of Data Access Governance Reports
Data access governance reports give you a generalized overview of sharing activity and can serve as a starting point for further investigation. However, in order to draw any useful conclusions from these figures, you need additional context that snapshot and activity reports do not provide.
For example, a site having a high number of new sharing links by itself does not tell you whether users are being careless or simply onboarding a new supplier this month. The fact that these reports do not allow you to drill down into details limits their usefulness, effectively leaving you to play detective on your own.
Advantages:
Global readout of entire M365 tenant
Bird’s eye view of sharing activity
Disadvantages:
Shows sharing hot spots but no context
You have to investigate what is being shared
Leaves you to identify problems yourself
Data access governance reports can also be managed through PowerShell using the cmdlet Start-SPODataAccessGovernanceInsight.
Microsoft 365 Access Governance in tenfold: See how it works!
Site-Level Sharing Reports
Aside from the tenant-wide data access governance reports, Microsoft 365 also allows you to generate site-level file and folder sharing reports for SharePoint sites and personal OneDrives. These reports are exported as a CSV table listing every file and folder in that SharePoint site and who has access to it. It also shows the file type, permission level and whether it was shared with an internal or external user.
How to run the file sharing report in SharePoint:
Open Microsoft 365 in your browser
Go to the SharePoint site you want to run a report on
Click on the gear icon and click on Site Usage
Scroll to the bottom under Shared with external users and click Run report
Despite the heading “Shared with external users”, the report covers both internal and external sharing.
How to run the file sharing report in OneDrive:
Open OneDrive in your browser
Click on the gear icon and click on OneDrive settings
Click on More settings on the left-hand side
Click on Run sharing report under Manage access
Advantages & Disadvantages of Site-Level Sharing Reports
Unlike tenant-wide data access governance reports, site-level sharing reports actually show you which files and folders your users are sharing. This in-depth breakdown provides crucial context to investigate possible instances of unwanted sharing or cloud data leakage: By drilling down to the object-level, admins can determine exactly who has access to shared data.
The main downside of sharing reports is their limited usability. Since each report covers just one site in your tenant, piecing together the whole picture might require you to sift through dozens or hundreds of reports. Even within a single report, it’s easy to miss important information while scanning past obvious entries for site owners or built-in Microsoft 365 groups. Unfortunately, site-level reports are still not quite the central sharing dashboard M365 admins are looking for.
Advantages:
Detailed list of each shared file
Object-level breakdown of access
Disadvantages:
Must be generated manually for each site
Can be difficult to sift through
Site Access Reviews in Microsoft 365
Site access reviews in Microsoft 365 allow admins to delegate the process of reviewing data access governance reports to site owners. This is useful both to free up IT staff from needing to audit your entire tenant by themselves and because site owners have a better understanding of who needs access to data that lives in their site.
In essence, site access reviews provide an in-depth version of data access governance reports limited to a specific SharePoint site. Site access reviews are supported for the permission baseline report, content shared with EEEU report and sharing links reports. To initiate a site access review, follow the process below.
How to initiate a site access review in Microsoft 365:
Navigate to the SharePoint admin center
Open a supported Data Access Governance report
Choose the site(s) you want to trigger an access review for
Click on “Initiate site access review” above the report
Customize and then send the review request to site owners
Once you start a site access review, site owners receive an email notification with a link to a detailed review page based on the data access governance report your chose. For example, if you trigger a review for a site with a high number of sharing links created in the last 28 days, the site owner will be shown a list of files that have been shared via link in that time period.
This personal review page allows site owners to confirm whether shared access is appropriate and still required. If not, reviewers can take action directly from the review page clicking on “Manage access” to remove users, modify group memberships or delete links.
Once a site owner is done checking and updating access, they finish the process by clicking on “Complete review”. Before submitting, they can also leave a comment to provide additional context for admins, which can help inform future reviews.
Advantages and Disadvantages of Site Access Reviews
Site access reviews are a useful governance tool for controlling shared access, especially in larger environments. Delegating the review process to site owners ensures reviewers have the necessary context to make well-informed decisions about cloud access. Their familiarity with the users and files under review makes audits both faster and more accurate.
However, the usefulness of site access reviews varies by report type. For example, reviews based on sharing link reports give reviewers a list of all recently created sharing links, showing both the shared file and who created the link. On the other hand, reviews for the baseline permission report simply list items with a high number of privileged users. Site owners may have to investigate on their own to find out who exactly has access to these files and why.
Lastly, site access reviews only cover SharePoint sites and do not support OneDrive. This means that objects shared from a user’s OneDrive, such as files uploaded to a one-on-one chat in Teams, fall outside the scope of site access reviews. Currently, no comparable feature is available for OneDrive within Microsoft 365’s governance toolset.
Advantages:
Delegates review process to stakeholders
Pulls up relevant information for reviewers
Disadvantages:
Some review pages show limited context
Does not cover OneDrive sharing/links
Site Lifecycle Management Policies in Microsoft 365
Another governance feature available through SharePoint Advanced Management, site lifecycle management policies help organizations identify ownerless or inactive SharePoint sites. This allows you to limit content sprawl and archive sites that no longer serve a business purpose, reducing the scale of your M365 tenant.
There are three policy types you can set up to help manage site lifecycles:
Inactive site policy: Identifies sites where no activity has taken place for a period of X months either directly in SharePoint or through connected apps like Teams, Exchange or Viva Engage. Enforced in three configurable stages: First, site owners are notified of inactivity. After three unaddressed notifications, sites can be switched to read-only mode. Finally, if no action is taken, sites can be automatically archived.
Site ownership policy: Identifies sites that do not meet your required number of owners and admins, allowing you to prompt managers or active users to claim ownership. Sites that continue to fall short of owner/admin requirements can be switched to read-only. However, automated archival is only supported for sites with zero owners.
Site attestation policy: Requires site owners to verify that their site is still in use and meets governance and/or business requirements. Site owners receive a customizable email message and must certify their site for continued use. Can be set up to require recurring attestation by site owners.
While site policies do not give you insight into shared access directly, they can help you prevent shared access from persisting longer than intended by eliminating inactive, unmanaged or ownerless sites.
Audit Sharing Events with Microsoft Purview
Organizations that have enabled audit logging through Microsoft Purview can also use the collected data to identify events related to cloud sharing. Aside from the FileAccessed event that is recorded any time a user opens a file in SharePoint or OneDrive, there are various event types that relate specifically to shared files:
SharingInvitationCreated: Triggers when a user in your organization shares a resource with an external user.
SharingInvitationAccepted: Triggers when an external user accepts the sharing invitation they have received, meaning they now have access to the resource.
AnonymousLinkCreated: Triggers when an anonymous Anyone link for a shared file is created.
AnonymousLinkUsed: Triggers when an anonymous Anonye link for a shared file is used.
SecureLinkCreated: Triggers when a user shares a resource through a specific people link.
AddedtoSecureLink: Identifies the (external) users that have been invited through a specific people link to access a shared resource.
Audit logs in Purview can be an important source of data for cloud sharing events. However, they are more suitable for narrow forensic analysis than a consistent overview of sharing activity. Keep in mind that Purview requires an E5 subscription or paid add-on license.
tenfold: Access Governance for M365 & Beyond
As you can see, Microsoft 365 does offer some governance features for shared files: site-level sharing reports, broad data access governance reports and access reviews by site owners. These tools provide important if very basic guardrails to rein in oversharing, which can put sensitive data at risk of leaks or breaches without effective access control.
However, the built-in governance tools available in Microsoft 365 have a number of functional and usability limitations that can lead to visibility gaps. Here are just a few of the issues that leave many orgs frustrated with SharePoint’s native toolset:
No OneDrive coverage: Access reviews and access governance reports only analyze SharePoint sites, not data shared through OneDrive accounts.
No central dashboard for sharing activity: Information is split between global reports, site-level reports and site owner review pages, with admins having to cycle through different panels.
No granular visibility: Some reports provide object-level details, others only broad figures such as a count of total privileged users.
Limited reporting window: Reports take up to 24 hours to complete and only cover the last 28 days of activity. Snapshot reports can only be rerun after 30 days.
To sum up: While built-in governance tools provide some visibility into shared data, they still fall short of the all-in-one reporting platform M365 admins are looking for. If you want a unified access governance solution that provides in-depth insight into all areas of Microsoft 365, there is a better way!
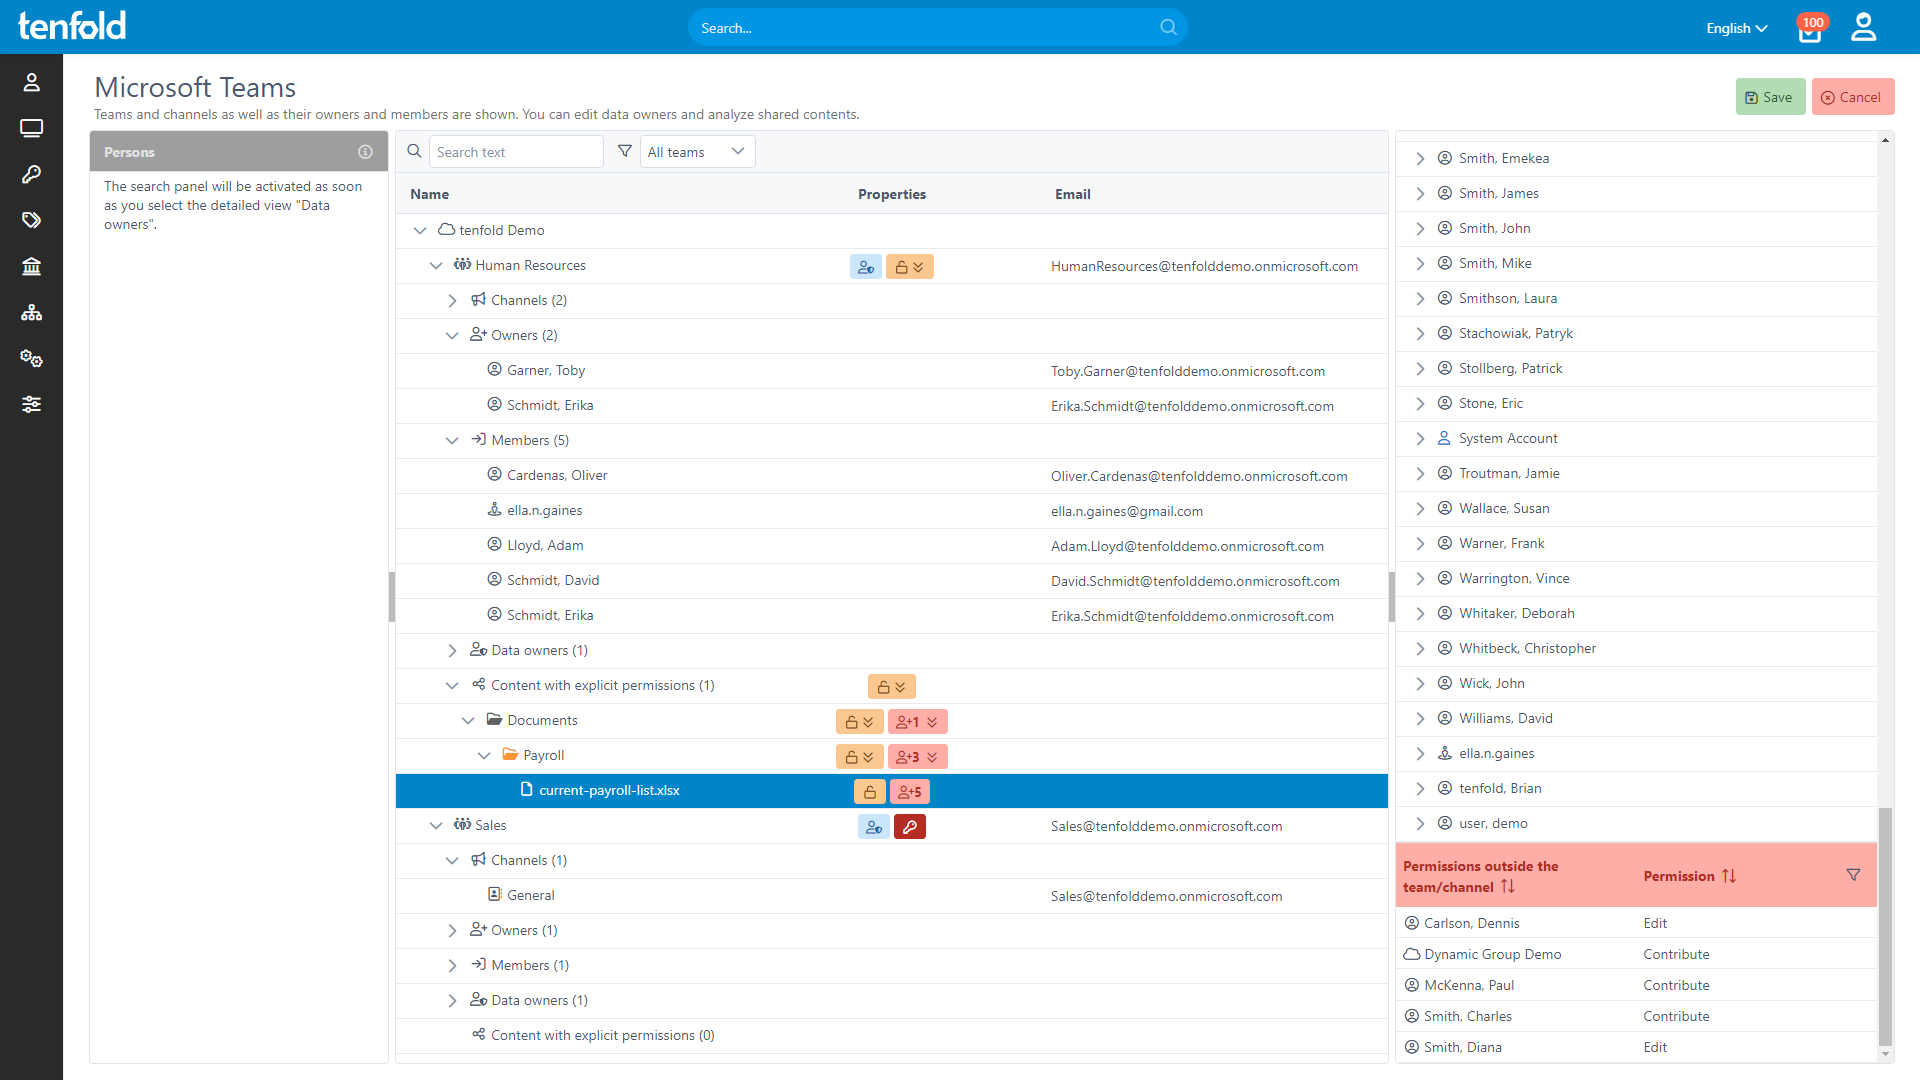
tenfold provides central reporting and access reviews for all files shared through Teams, OneDrive and SharePoint – and it integrates seamlessly with both cloud and on-prem Microsoft environments. With a no-code setup and out-of-the-box support for the apps you use, IGA has never been easier. See how it works with our in-browser demo or talk to our team to discuss your use case today!